
Integrations & API
Pro feature
Webhooks: Connect Zapier, Make, n8n & Slack
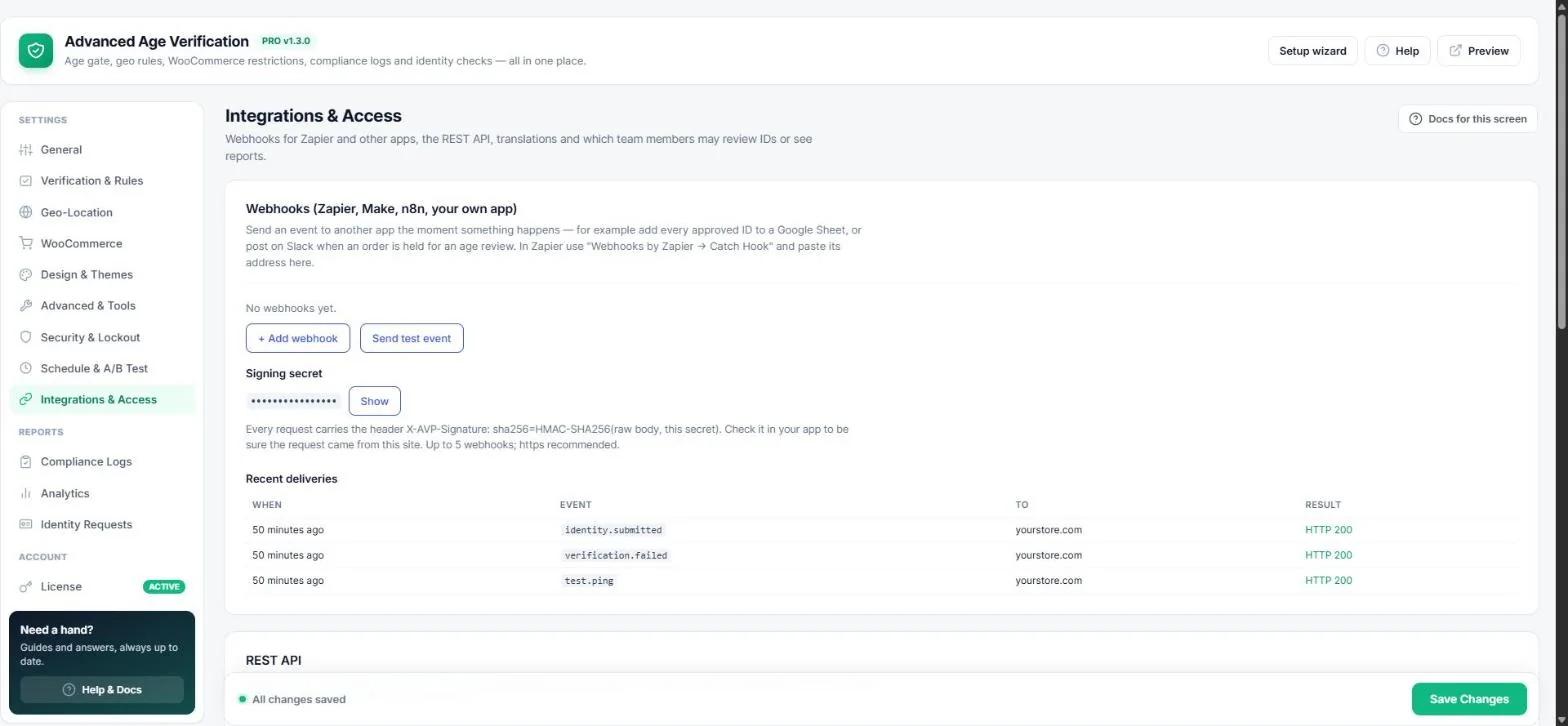
Send an event to another app the moment something happens — add every approved ID to a Google Sheet, post on Slack when an order is held for an age review, or update your CRM. Open Age Verification → Integrations & Access.
Add a webhook
- Create a catch URL in your app — in Zapier use Webhooks by Zapier → Catch Hook, in Make a Custom webhook, in n8n a Webhook node.
- Click + Add webhook, paste the URL and tick the events you want.
- Save, then click Send test event. The result appears under Recent deliveries.
You can add up to 5 webhooks; https:// addresses are recommended.
Events
| Event | When it fires |
|---|---|
verification.passed | A visitor passed the age gate (can be high volume). |
verification.failed | A visitor was underage or entered an invalid age. |
idcheck.passed / idcheck.failed | Result of a provider ID check (Stripe, Veriff, AgeChecker). |
identity.submitted | A visitor uploaded an ID document. |
identity.approved / identity.rejected | You reviewed an ID document. |
order.age_hold | A WooCommerce order was put on hold for an age review. |
lockout | A visitor was locked out after a failed check. |
Payload
{
  "id": "6f1c…",
  "event": "order.age_hold",
  "created_at": "2026-11-12T13:05:32+00:00",
  "site": { "name": "Your Store", "url": "https://yourstore.com/" },
  "data": { "order_id": 1042, "order_number": "1042", "age": 19, "required_age": 21, "edit_url": "…" }
}
Visitor events also include country and a masked IP (ip_masked). Headers: X-AVP-Event, X-AVP-Delivery and X-AVP-Signature.
Verify the signature
Every request is signed with your signing secret: X-AVP-Signature: sha256=HMAC-SHA256(raw body, secret).
$expected = 'sha256=' . hash_hmac('sha256', file_get_contents('php://input'), $secret);
if (! hash_equals($expected, $_SERVER['HTTP_X_AVP_SIGNATURE'] ?? '')) {
    http_response_code(401); exit;
}
Note: Webhooks are sent after the visitor's page has loaded, so they never slow your site down.
Read next
Was this guide helpful?
Thanks for your feedback!